Encrypted down to the station
Nobody reads along between station and application. Charging stations connect over an encrypted connection only.
Every station signs in with credentials of its own, and every message is validated before it takes effect.
Encrypted connectionValidated messagesOperated in GermanyWhat holds between the charging station and the screen.
Nobody reads along between station and application. Charging stations connect over an encrypted connection only.
A leaked ID opens one station at most. An ID and a password are valid for exactly one charging station.
The stored value cannot be turned back into a password. It appears once and stays unreadable afterwards.
A faulty message does no damage. Every message is validated against the official OCPP 1.6 schemas.
Read more →An organisation sees its own charge points, cards and drivers, and nothing else.
Read more →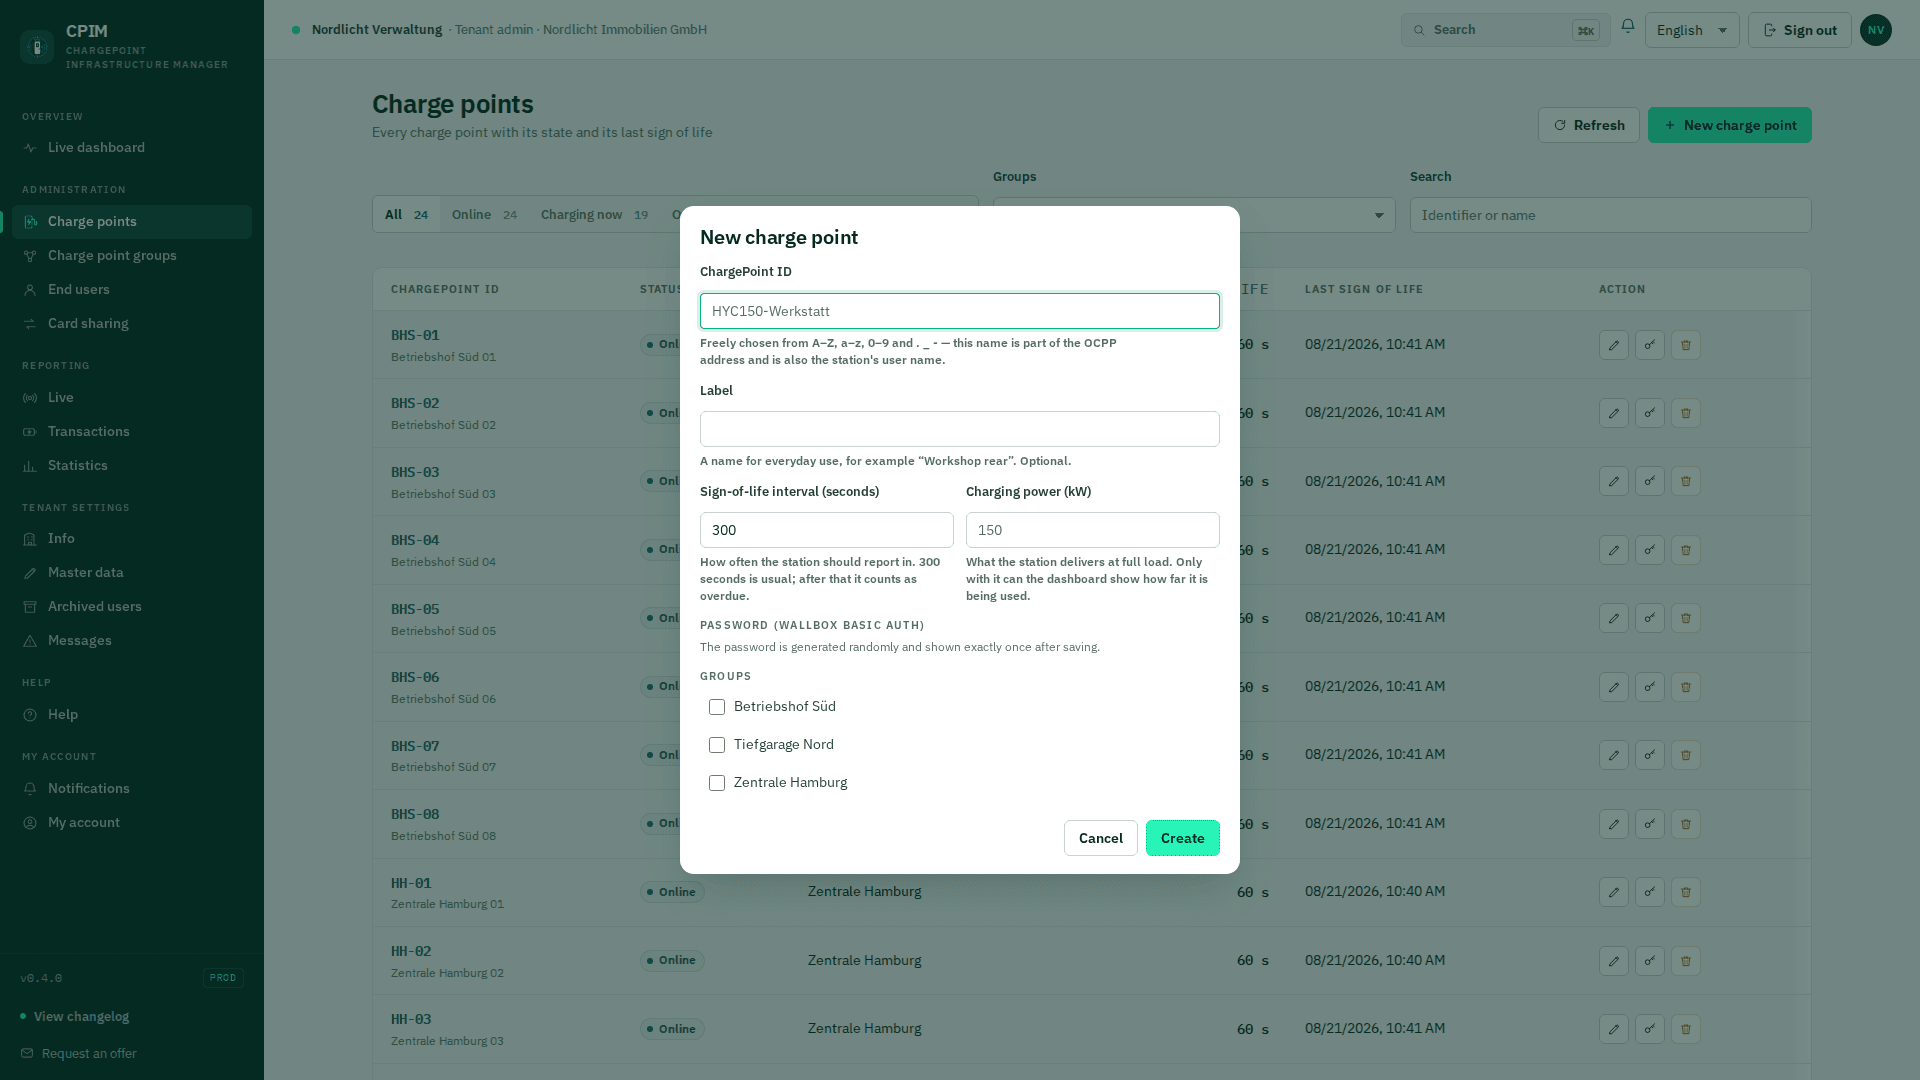
The application talks to the charging stations and to the browser, and to nobody else.
Over an encrypted connection with an ID and password of its own. Wrong details fail during the handshake.
It is generated again and shown once. The station receives the new value in its configuration.
No. Each organisation sees its own records, and there is no reporting across organisations.
The energy charged per provider. The card number and the person stay hidden.
No. Accounts live in the installation itself. A second factor is planned and not included today.
Unreadable in the database. A lost password is generated again, never read out.
Send the questions your review asks, and a human will answer them.
Prefer e-mail? info@dstech-it.de